Initial triage
I decided to use DetectItEasy on the sample first:
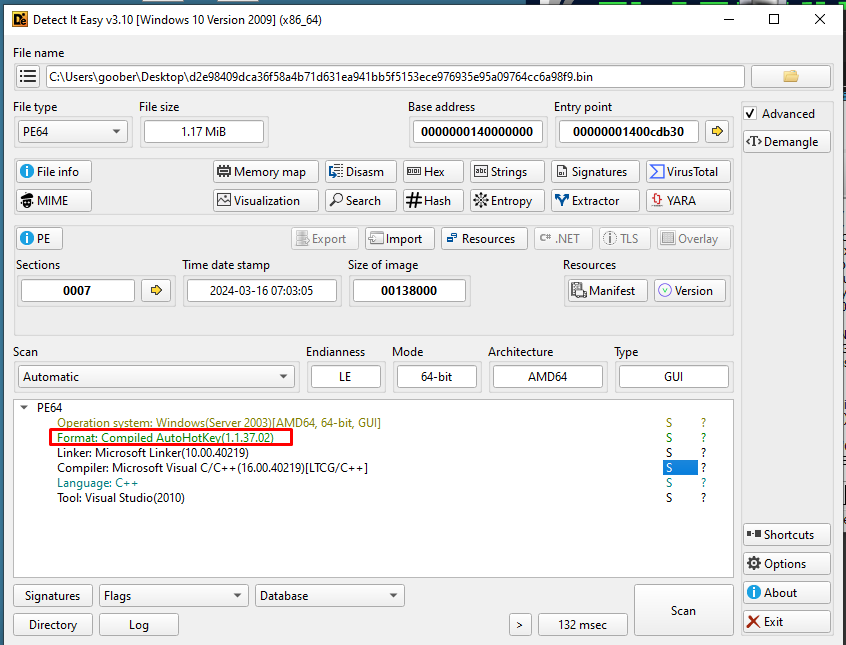
And this revealed the file was a compiled AutoHotKey script. I searched on possibilities of extracting the original AHK script from it, and found this Reddit comment that said:
If the executable is "compiled" with AHK_H and the source code is encrypted you're out of luck.
With Resource Hacker you can have the script as a resource. If the .exe is compressed you only need to decompress or just the Payload Decompiler is been around for ages.
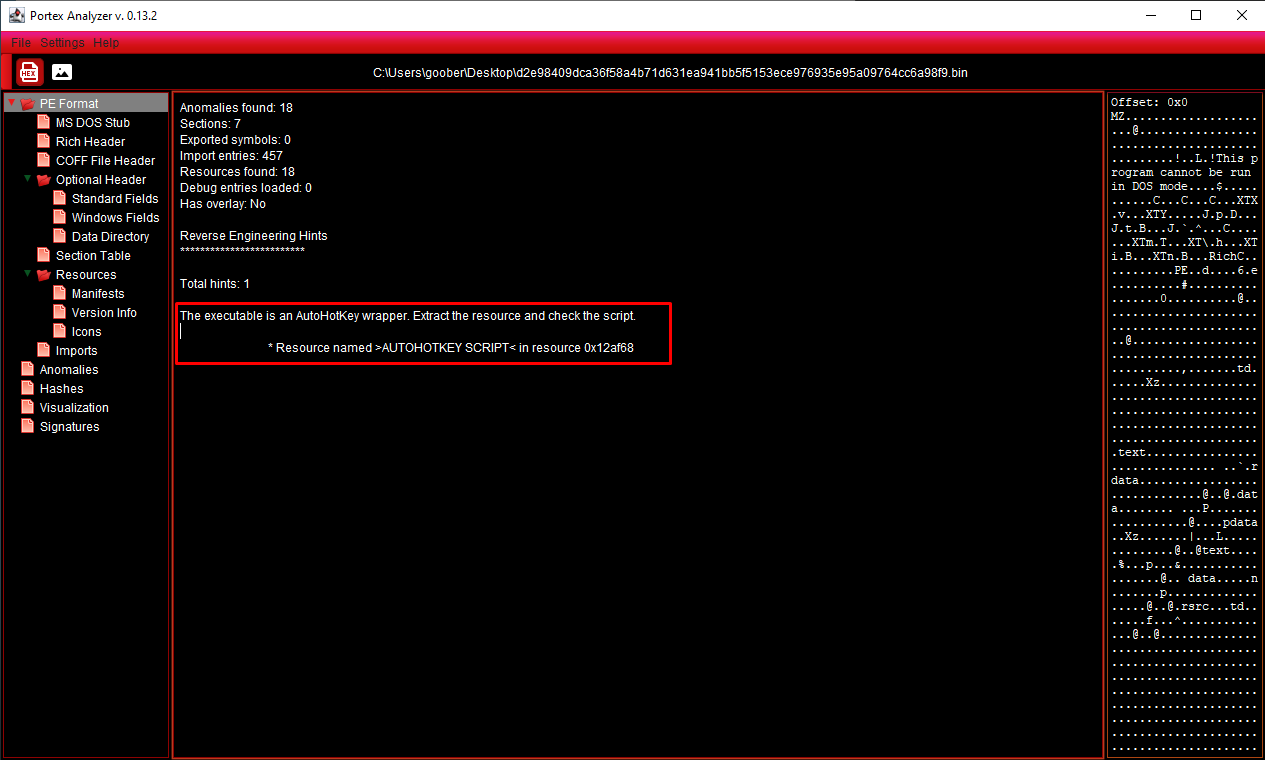
I have also used Portex Analyzer which told me the same tip:
Script extraction
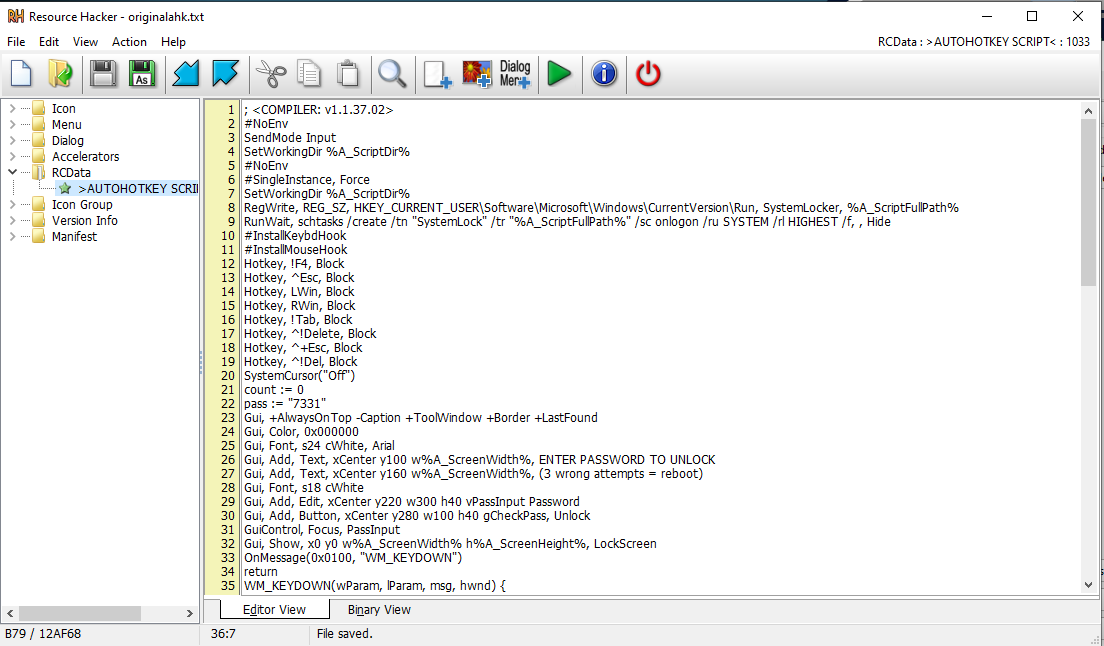
So I decided to open Resource Hacker, opened the RCData tab and there was the AHK script:
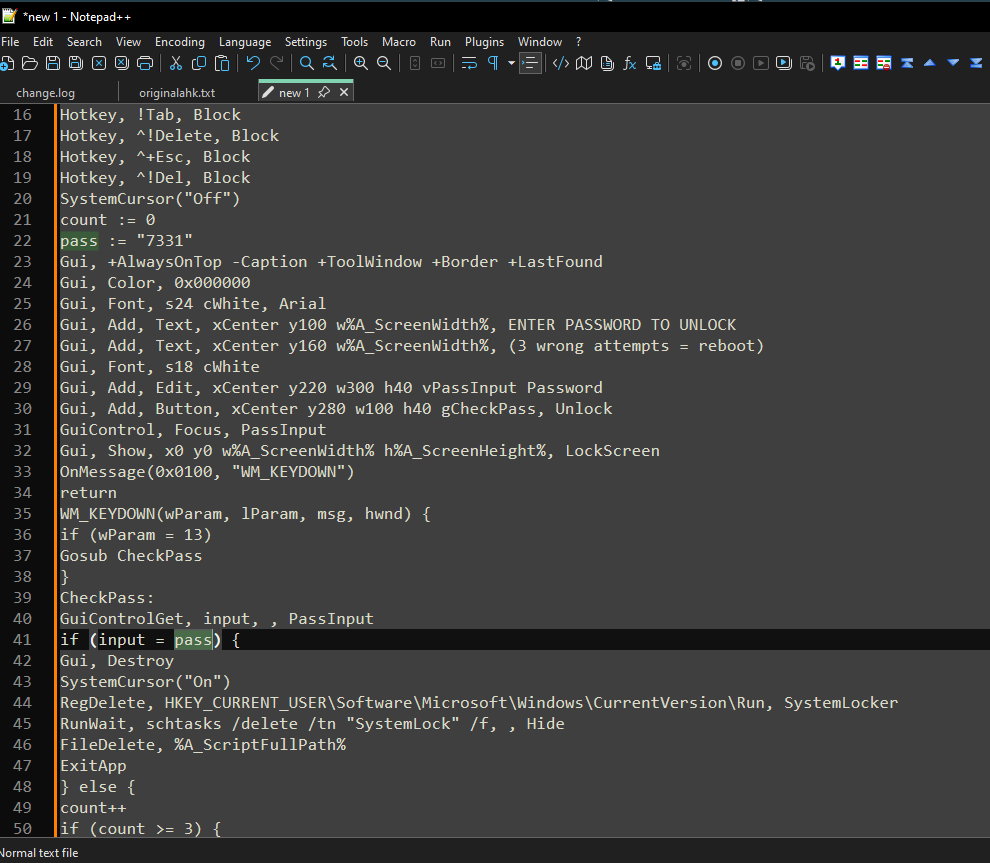
I copied and pasted the script in NP++ and discovered the password is 7331. :D