Summary
The file is a malicious Microsoft Excel file with a document exploit to retrieve resources from a remote location.
General
Hashes
| Type | Hash |
|---|---|
| MD5 | 84015d951644de3ccb491f77777e5bd4 |
| SHA1 | 84f4fe84c87c3b621da0db664af003cdb1d882be |
| SHA256 | 478d992c999a0e93ada1c9aa10644e3abdc207d407492c5bc2710986de4d42be |
Triage
The file command indicates that we are dealing with an Excel file:
$ file 478d992c999a0e93ada1c9aa10644e3abdc207d407492c5bc2710986de4d42be
478d992c999a0e93ada1c9aa10644e3abdc207d407492c5bc2710986de4d42be: Composite Document File V2 Document, Little Endian, Os: Windows, Version 6.2, Code page: 1252, Name of Creating Application: Microsoft Excel, Create Time/Date: Sat Sep 16 00:00:00 2006, Last Saved Time/Date: Wed Apr 22 06:26:11 2026, Security: 1
Exiftool indicates that the document was created on 2006:09:16 00:00:00
$ exiftool sample/478d992c999a0e93ada1c9aa10644e3abdc207d407492c5bc2710986de4d42be
ExifTool Version Number         : 13.59
File Name                       : 478d992c999a0e93ada1c9aa10644e3abdc207d407492c5bc2710986de4d42be
Directory                       : sample
File Size                       : 719 kB
File Modification Date/Time     : 2026:04:23 15:42:02+00:00
File Access Date/Time           : 2026:09:15 08:47:01+00:00
File Inode Change Date/Time     : 2026:09:15 08:46:53+00:00
File Permissions                : -rw-rw-r--
File Type                       : XLS
File Type Extension             : xls
MIME Type                       : application/vnd.ms-excel
Author                          :
Last Modified By                :
Software                        : Microsoft Excel
Create Date                     : 2006:09:16 00:00:00
Modify Date                     : 2026:04:22 06:26:11
Security                        : Password protected
Code Page                       : Windows Latin 1 (Western European)
App Version                     : 12.0000
Scale Crop                      : No
Links Up To Date                : No
Shared Doc                      : No
Hyperlinks Changed              : No
Title Of Parts                  : Sheet1, Sheet2, Sheet3
Heading Pairs                   : Worksheets, 3
Comp Obj User Type Len          : 38
Comp Obj User Type              : Microsoft Office Excel 2003 Worksheet
oletimes, however, only indicates creation timestamps in 2026:
$ oletimes sample/478d992c999a0e93ada1c9aa10644e3abdc207d407492c5bc2710986de4d42be
oletimes 0.54 - http://decalage.info/python/oletools
THIS IS WORK IN PROGRESS - Check updates regularly!
Please report any issue at https://github.com/decalage2/oletools/issues
===============================================================================
FILE: sample/478d992c999a0e93ada1c9aa10644e3abdc207d407492c5bc2710986de4d42be

+----------------------------+---------------------+---------------------+
| Stream/Storage name        | Modification Time   | Creation Time       |
+----------------------------+---------------------+---------------------+
| Root                       | 2026-04-22 06:26:11 | None                |
| '\x01CompObj'              | None                | None                |
| '\x05DocumentSummaryInform | None                | None                |
| ation'                     |                     |                     |
| '\x05SummaryInformation'   | None                | None                |
| 'MBD00ABFD2F'              | 2026-04-22 06:26:10 | 2026-04-22 06:26:10 |
| 'MBD00ABFD2F/\x01CompObj'  | None                | None                |
| 'MBD00ABFD2F/Package'      | None                | None                |
| 'MBD00ABFD30'              | 2026-04-22 06:26:10 | 2026-04-22 06:26:10 |
| 'MBD00ABFD30/\x01Ole'      | None                | None                |
| 'Workbook'                 | None                | None                |
| '_VBA_PROJECT_CUR'         | 2026-04-22 06:26:11 | 2026-04-22 06:26:10 |
| '_VBA_PROJECT_CUR/PROJECT' | None                | None                |
| '_VBA_PROJECT_CUR/PROJECTw | None                | None                |
| m'                         |                     |                     |
| '_VBA_PROJECT_CUR/VBA'     | 2026-04-22 06:26:11 | 2026-04-22 06:26:11 |
| '_VBA_PROJECT_CUR/VBA/Shee | None                | None                |
| t1'                        |                     |                     |
| '_VBA_PROJECT_CUR/VBA/Shee | None                | None                |
| t2'                        |                     |                     |
| '_VBA_PROJECT_CUR/VBA/Shee | None                | None                |
| t3'                        |                     |                     |
| '_VBA_PROJECT_CUR/VBA/This | None                | None                |
| Workbook'                  |                     |                     |
| '_VBA_PROJECT_CUR/VBA/_VBA | None                | None                |
| _PROJECT'                  |                     |                     |
| '_VBA_PROJECT_CUR/VBA/dir' | None                | None                |
+----------------------------+---------------------+---------------------+
Static Analysis
Given that it is an Excel file, we will use ole tools for the analysis.
oleid indicates the presence of macros:
$ oleid 478d992c999a0e93ada1c9aa10644e3abdc207d407492c5bc2710986de4d42be
oleid 0.60.1 - http://decalage.info/oletools
THIS IS WORK IN PROGRESS - Check updates regularly!
Please report any issue at https://github.com/decalage2/oletools/issues

Filename: 478d992c999a0e93ada1c9aa10644e3abdc207d407492c5bc2710986de4d42be
WARNING  For now, VBA stomping cannot be detected for files in memory
--------------------+--------------------+----------+--------------------------
Indicator           |Value               |Risk      |Description
--------------------+--------------------+----------+--------------------------
File format         |MS Excel 97-2003    |info      |
                    |Workbook or Template|          |
--------------------+--------------------+----------+--------------------------
Container format    |OLE                 |info      |Container type
--------------------+--------------------+----------+--------------------------
Application name    |Microsoft Excel     |info      |Application name declared
                    |                    |          |in properties
--------------------+--------------------+----------+--------------------------
Properties code page|1252: ANSI Latin 1; |info      |Code page used for
                    |Western European    |          |properties
                    |(Windows)           |          |
--------------------+--------------------+----------+--------------------------
Encrypted           |True                |low       |The file is encrypted. It
                    |                    |          |may be decrypted with
                    |                    |          |msoffcrypto-tool
--------------------+--------------------+----------+--------------------------
VBA Macros          |Yes                 |Medium    |This file contains VBA
                    |                    |          |macros. No suspicious
                    |                    |          |keyword was found. Use
                    |                    |          |olevba and mraptor for
                    |                    |          |more info.
--------------------+--------------------+----------+--------------------------
XLM Macros          |No                  |none      |This file does not contain
                    |                    |          |Excel 4/XLM macros.
--------------------+--------------------+----------+--------------------------
External            |0                   |none      |External relationships
Relationships       |                    |          |such as remote templates,
                    |                    |          |remote OLE objects, etc
--------------------+--------------------+----------+--------------------------
olevba only shows empty macros, so this investigative lead is a dead end.
Another option would be to decrypt the file, as oleid also indicates that the file encrypted.
To decrypt the file using msoffcrypto-tool, we would need the password.
First, we'll have a look into the file by extracting its contents:
$ mkdir out
$ 7z x 478d992c999a0e93ada1c9aa10644e3abdc207d407492c5bc2710986de4d42be -oout
Looking at the strings in the different extracted files, a suspicious URL can be found:
$ strings -n 8 -e l out/MBD00ABFD30/\[1\]Ole
https://s.klinikpintar.id/mamZ2f?&https://developers.cloudflare.com/workers/tutorials/?_gl=1*1gvugqd*_gcl_au*NTg0NjYzOTU5LjE3NzY2NzI0MjA.*_ga*YjEzZDVjZDItMTBlMy00ODJhLTliNTMtN2QyY2VmYmU5Njcx
9jgOFe4B5AkQCNhCke9Ov0ebUzsk5hWGVbaRY77zoqmKttxyAXf4wZnSVb8IYFMCzsADYxpWaf4xceBDb90phbmhT5Pkhl
The corresponding domain s.klinikpintar[.]id is flagged as malicious on Virustotal:
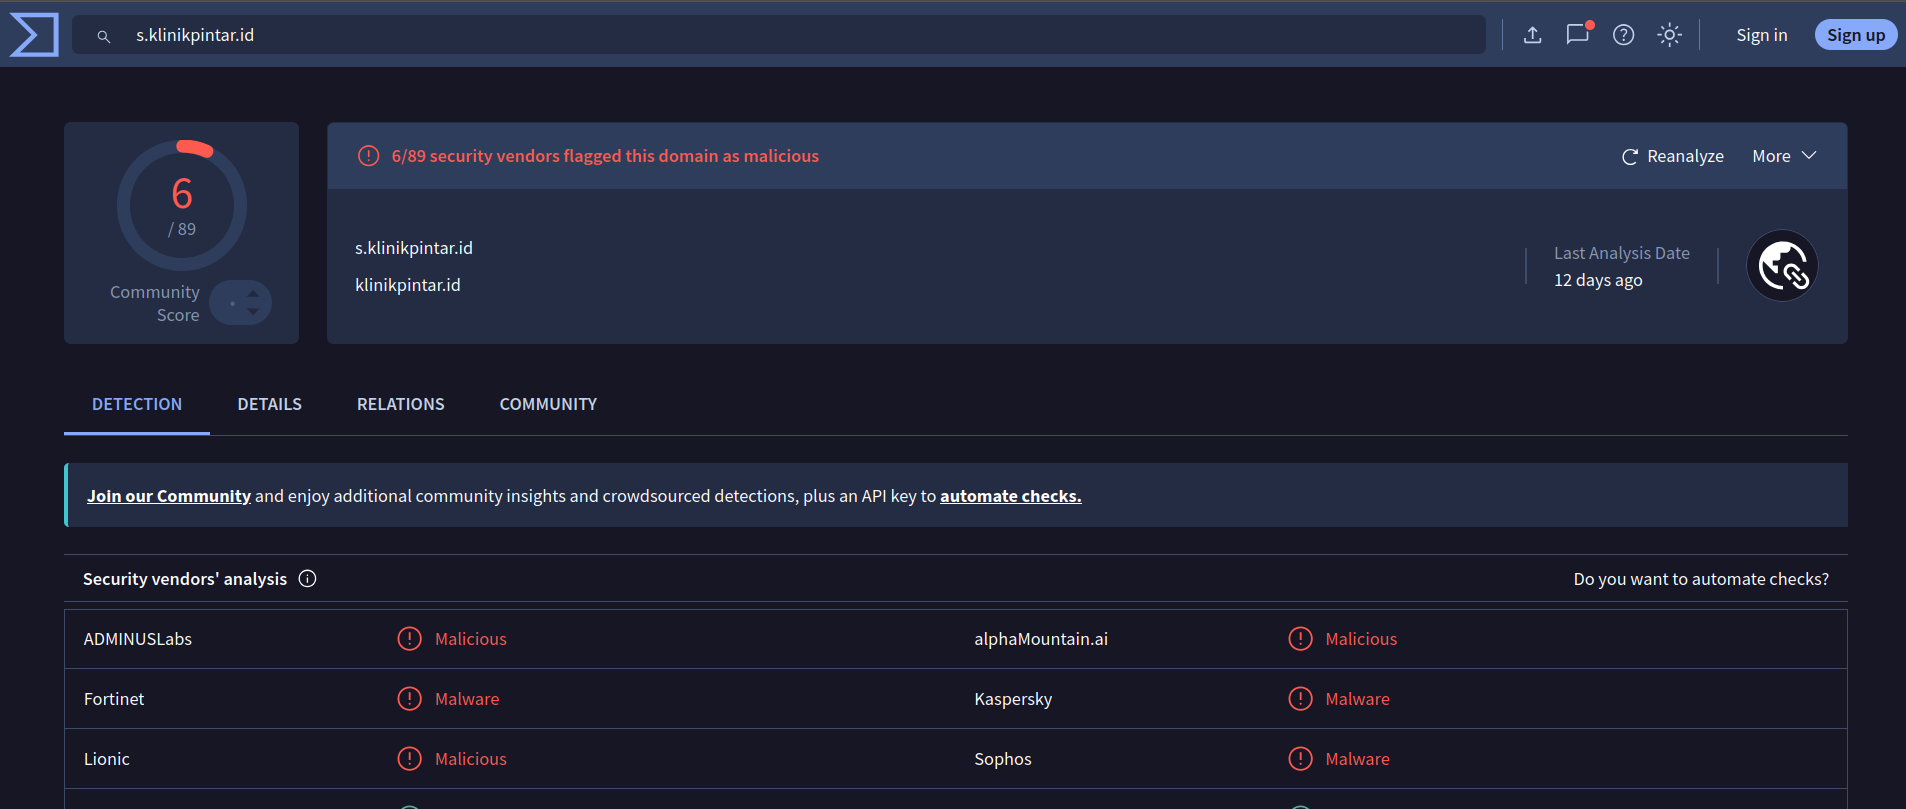
The registration date of that parent domain is 2019-04-10T11:43:27Z which is thirteen (13) years after the alleged document creation.
This could indicate that the creation timestamp has been tampered with.
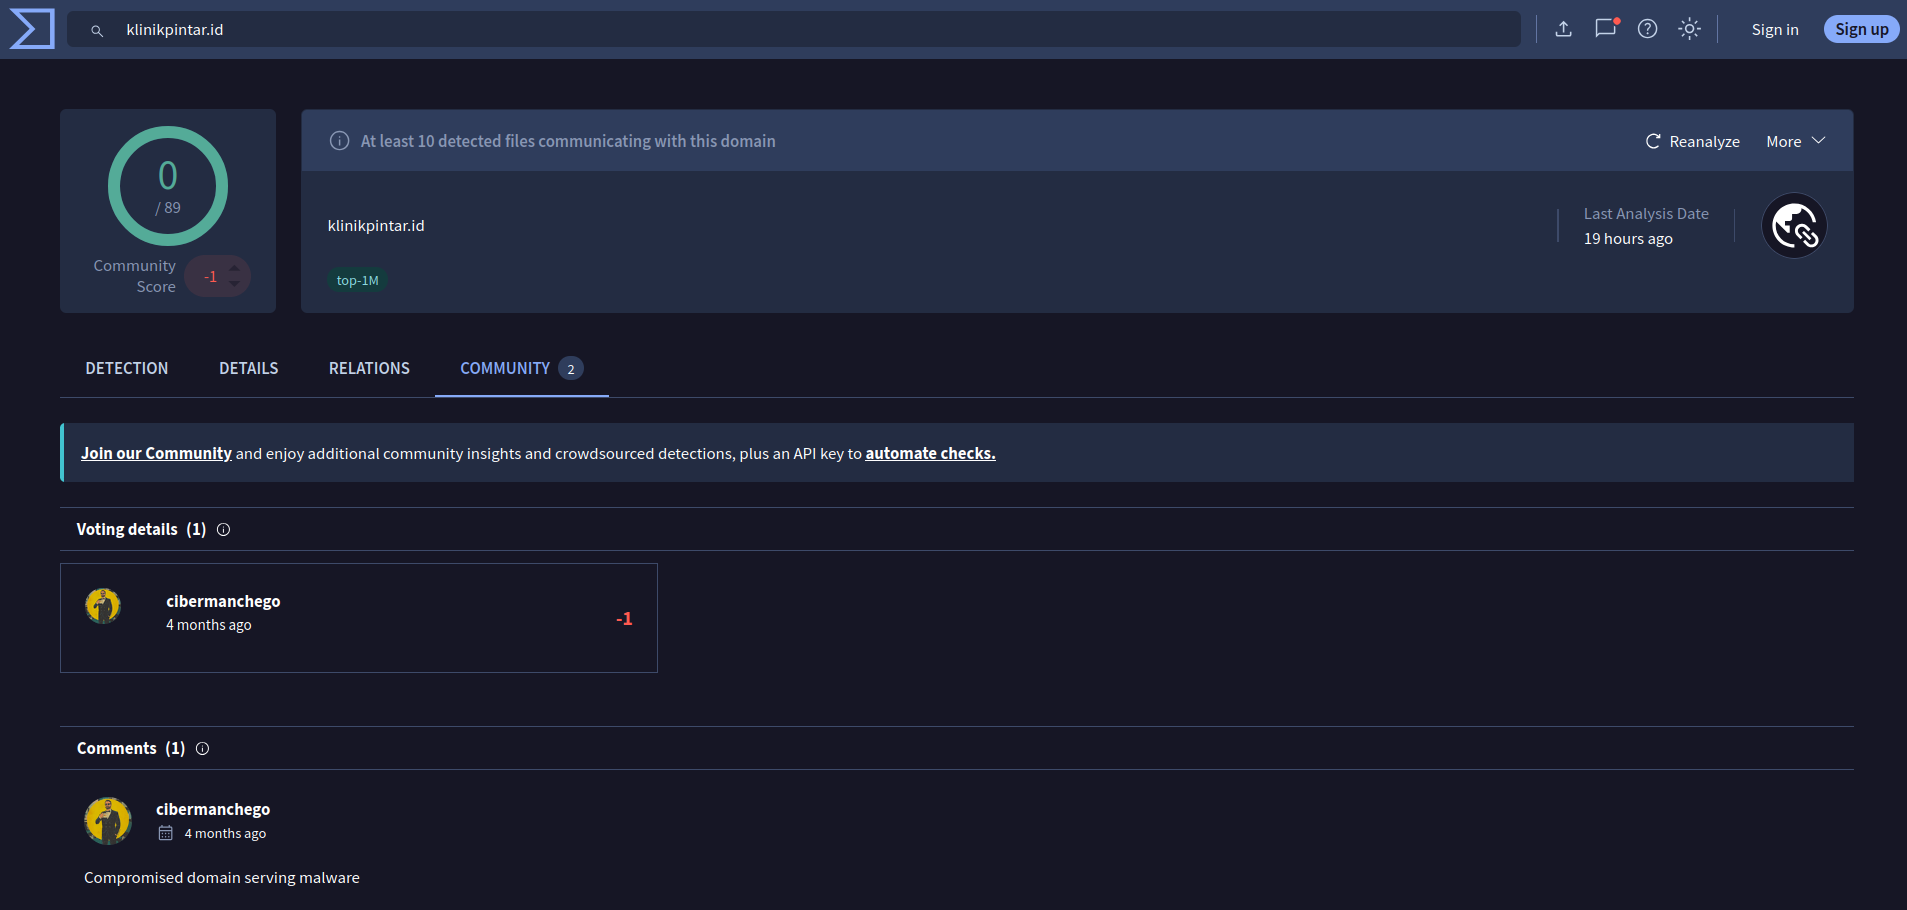
Comments on the Virustotal page indicate that this domain might be a compromised site that is abused to serve malware:
So far, we have only extracted the URL using string search but do not really know how the connection to that URL is performed.
Running oledir hints at the exploitation of a vulnerability:
$ oledir sample/478d992c999a0e93ada1c9aa10644e3abdc207d407492c5bc2710986de4d42be
oledir 0.54 - http://decalage.info/python/oletools
OLE directory entries in file sample/478d992c999a0e93ada1c9aa10644e3abdc207d407492c5bc2710986de4d42be:
----+------+-------+----------------------+-----+-----+-----+--------+------
id  |Status|Type   |Name                  |Left |Right|Child|1st Sect|Size
----+------+-------+----------------------+-----+-----+-----+--------+------
0   |<Used>|Root   |Root Entry            |-    |-    |3    |545     |9792
1   |<Used>|Stream |Workbook              |19   |-    |-    |548     |15449
2   |<Used>|Storage|_VBA_PROJECT_CUR      |4    |17   |16   |0       |0
3   |<Used>|Storage|MBD00ABFD2F           |1    |2    |5    |0       |0
4   |<Used>|Storage|MBD00ABFD30           |-    |-    |7    |0       |0
5   |<Used>|Stream |Package               |-    |6    |-    |D       |683179
6   |<Used>|Stream |\x01CompObj           |-    |-    |-    |0       |99
7   |<Used>|Stream |\x01Ole               |-    |-    |-    |2       |928
8   |<Used>|Storage|VBA                   |-    |-    |11   |0       |0
9   |<Used>|Stream |ThisWorkbook          |12   |13   |-    |11      |985
10  |<Used>|Stream |Sheet1                |14   |-    |-    |21      |977
11  |<Used>|Stream |Sheet2                |10   |9    |-    |31      |977
12  |<Used>|Stream |Sheet3                |-    |-    |-    |41      |977
13  |<Used>|Stream |_VBA_PROJECT          |-    |-    |-    |51      |2644
14  |<Used>|Stream |dir                   |-    |-    |-    |7B      |553
15  |<Used>|Stream |PROJECTwm             |-    |-    |-    |84      |104
16  |<Used>|Stream |PROJECT               |8    |15   |-    |86      |517
17  |<Used>|Stream |\x05SummaryInformation|-    |18   |-    |8F      |200
18  |<Used>|Stream |\x05DocumentSummaryInf|-    |-    |-    |93      |244
    |      |       |ormation              |     |     |     |        |
19  |<Used>|Stream |\x01CompObj           |-    |-    |-    |97      |114
----+----------------------------+------+--------------------------------------
id  |Name                        |Size  |CLSID
----+----------------------------+------+--------------------------------------
0   |Root Entry                  |-     |00020820-0000-0000-C000-000000000046
    |                            |      |Microsoft Microsoft Excel 97-2003
    |                            |      |Worksheet (Excel.Sheet.8)
19  |\x01CompObj                 |114   |
18  |\x05DocumentSummaryInformati|244   |
    |on                          |      |
17  |\x05SummaryInformation      |200   |
3   |MBD00ABFD2F                 |-     |00020830-0000-0000-C000-000000000046
    |                            |      |Microsoft Excel.Sheet.12
6   |  \x01CompObj               |99    |
5   |  Package                   |683179|
4   |MBD00ABFD30                 |-     |00000300-0000-0000-C000-000000000046
    |                            |      |StdOleLink (embedded OLE object -
    |                            |      |Known Related to CVE-2017-0199,
    |                            |      |CVE-2017-8570, CVE-2017-8759 or
    |                            |      |CVE-2018-8174)
7   |  \x01Ole                   |928   |
1   |Workbook                    |15449 |
2   |_VBA_PROJECT_CUR            |-     |
16  |  PROJECT                   |517   |
15  |  PROJECTwm                 |104   |
8   |  VBA                       |-     |
10  |    Sheet1                  |977   |
11  |    Sheet2                  |977   |
12  |    Sheet3                  |977   |
9   |    ThisWorkbook            |985   |
13  |    _VBA_PROJECT            |2644  |
14  |    dir                     |553   |
The lines of interest in the output are:
----+----------------------------+------+--------------------------------------
id  |Name                        |Size  |CLSID
----+----------------------------+------+--------------------------------------
[...]
4   |MBD00ABFD30                 |-     |00000300-0000-0000-C000-000000000046
    |                            |      |StdOleLink (embedded OLE object -
    |                            |      |Known Related to CVE-2017-0199,
    |                            |      |CVE-2017-8570, CVE-2017-8759 or
    |                            |      |CVE-2018-8174)
Information about the related CLSID can be found in the Microsoft documentation:
The OLEStream structure is contained inside an OLE Compound File Stream object ([MS-CFB] section 1.3). The name of this Compound File Stream object is "\1Ole". The stream object is contained within the OLE Compound File Storage object ([MS-CFB] section 1.3) corresponding to the linked object or embedded object (see section 1.3.3). The OLEStream structure specifies whether the storage object is for a linked object or an embedded object.
Notice that this matches with the embedded file name in which the URL was found: out/MBD00ABFD30/[1]Ole.
Vulnerabilities
Let us have a look at the vulnerabilities listed in the output of oledir.
All of them are remote code execution vulnerabilities that require an attacker to convince a user to open a specifically crafted file or visit a website.
CVE-2017-0199
A remote code execution vulnerability exists in the way that Microsoft Office and WordPad parse specially crafted files. An attacker who successfully exploited this vulnerability could take control of an affected system. An attacker could then install programs; view, change, or delete data; or create new accounts with full user rights.
CVE-2017-8570
A remote code execution vulnerability exists in Microsoft Office software when it fails to properly handle objects in memory. An attacker who successfully exploited the vulnerability could use a specially crafted file to perform actions in the security context of the current user. For example, the file could then take actions on behalf of the logged-on user with the same permissions as the current user.
CVE-2017-8759
A remote code execution vulnerability exists when Microsoft .NET Framework processes untrusted input. An attacker who successfully exploited this vulnerability in software using the .NET framework could take control of an affected system. An attacker could then install programs; view, change, or delete data; or create new accounts with full user rights. Users whose accounts are configured to have fewer user rights on the system could be less impacted than users who operate with administrative user rights.
CVE-2018-8174
A remote code execution vulnerability exists in the way that the VBScript engine handles objects in memory. The vulnerability could corrupt memory in such a way that an attacker could execute arbitrary code in the context of the current user. An attacker who successfully exploited the vulnerability could gain the same user rights as the current user. If the current user is logged on with administrative user rights, an attacker who successfully exploited the vulnerability could take control of an affected system. An attacker could then install programs; view, change, or delete data; or create new accounts with full user rights.